Overview
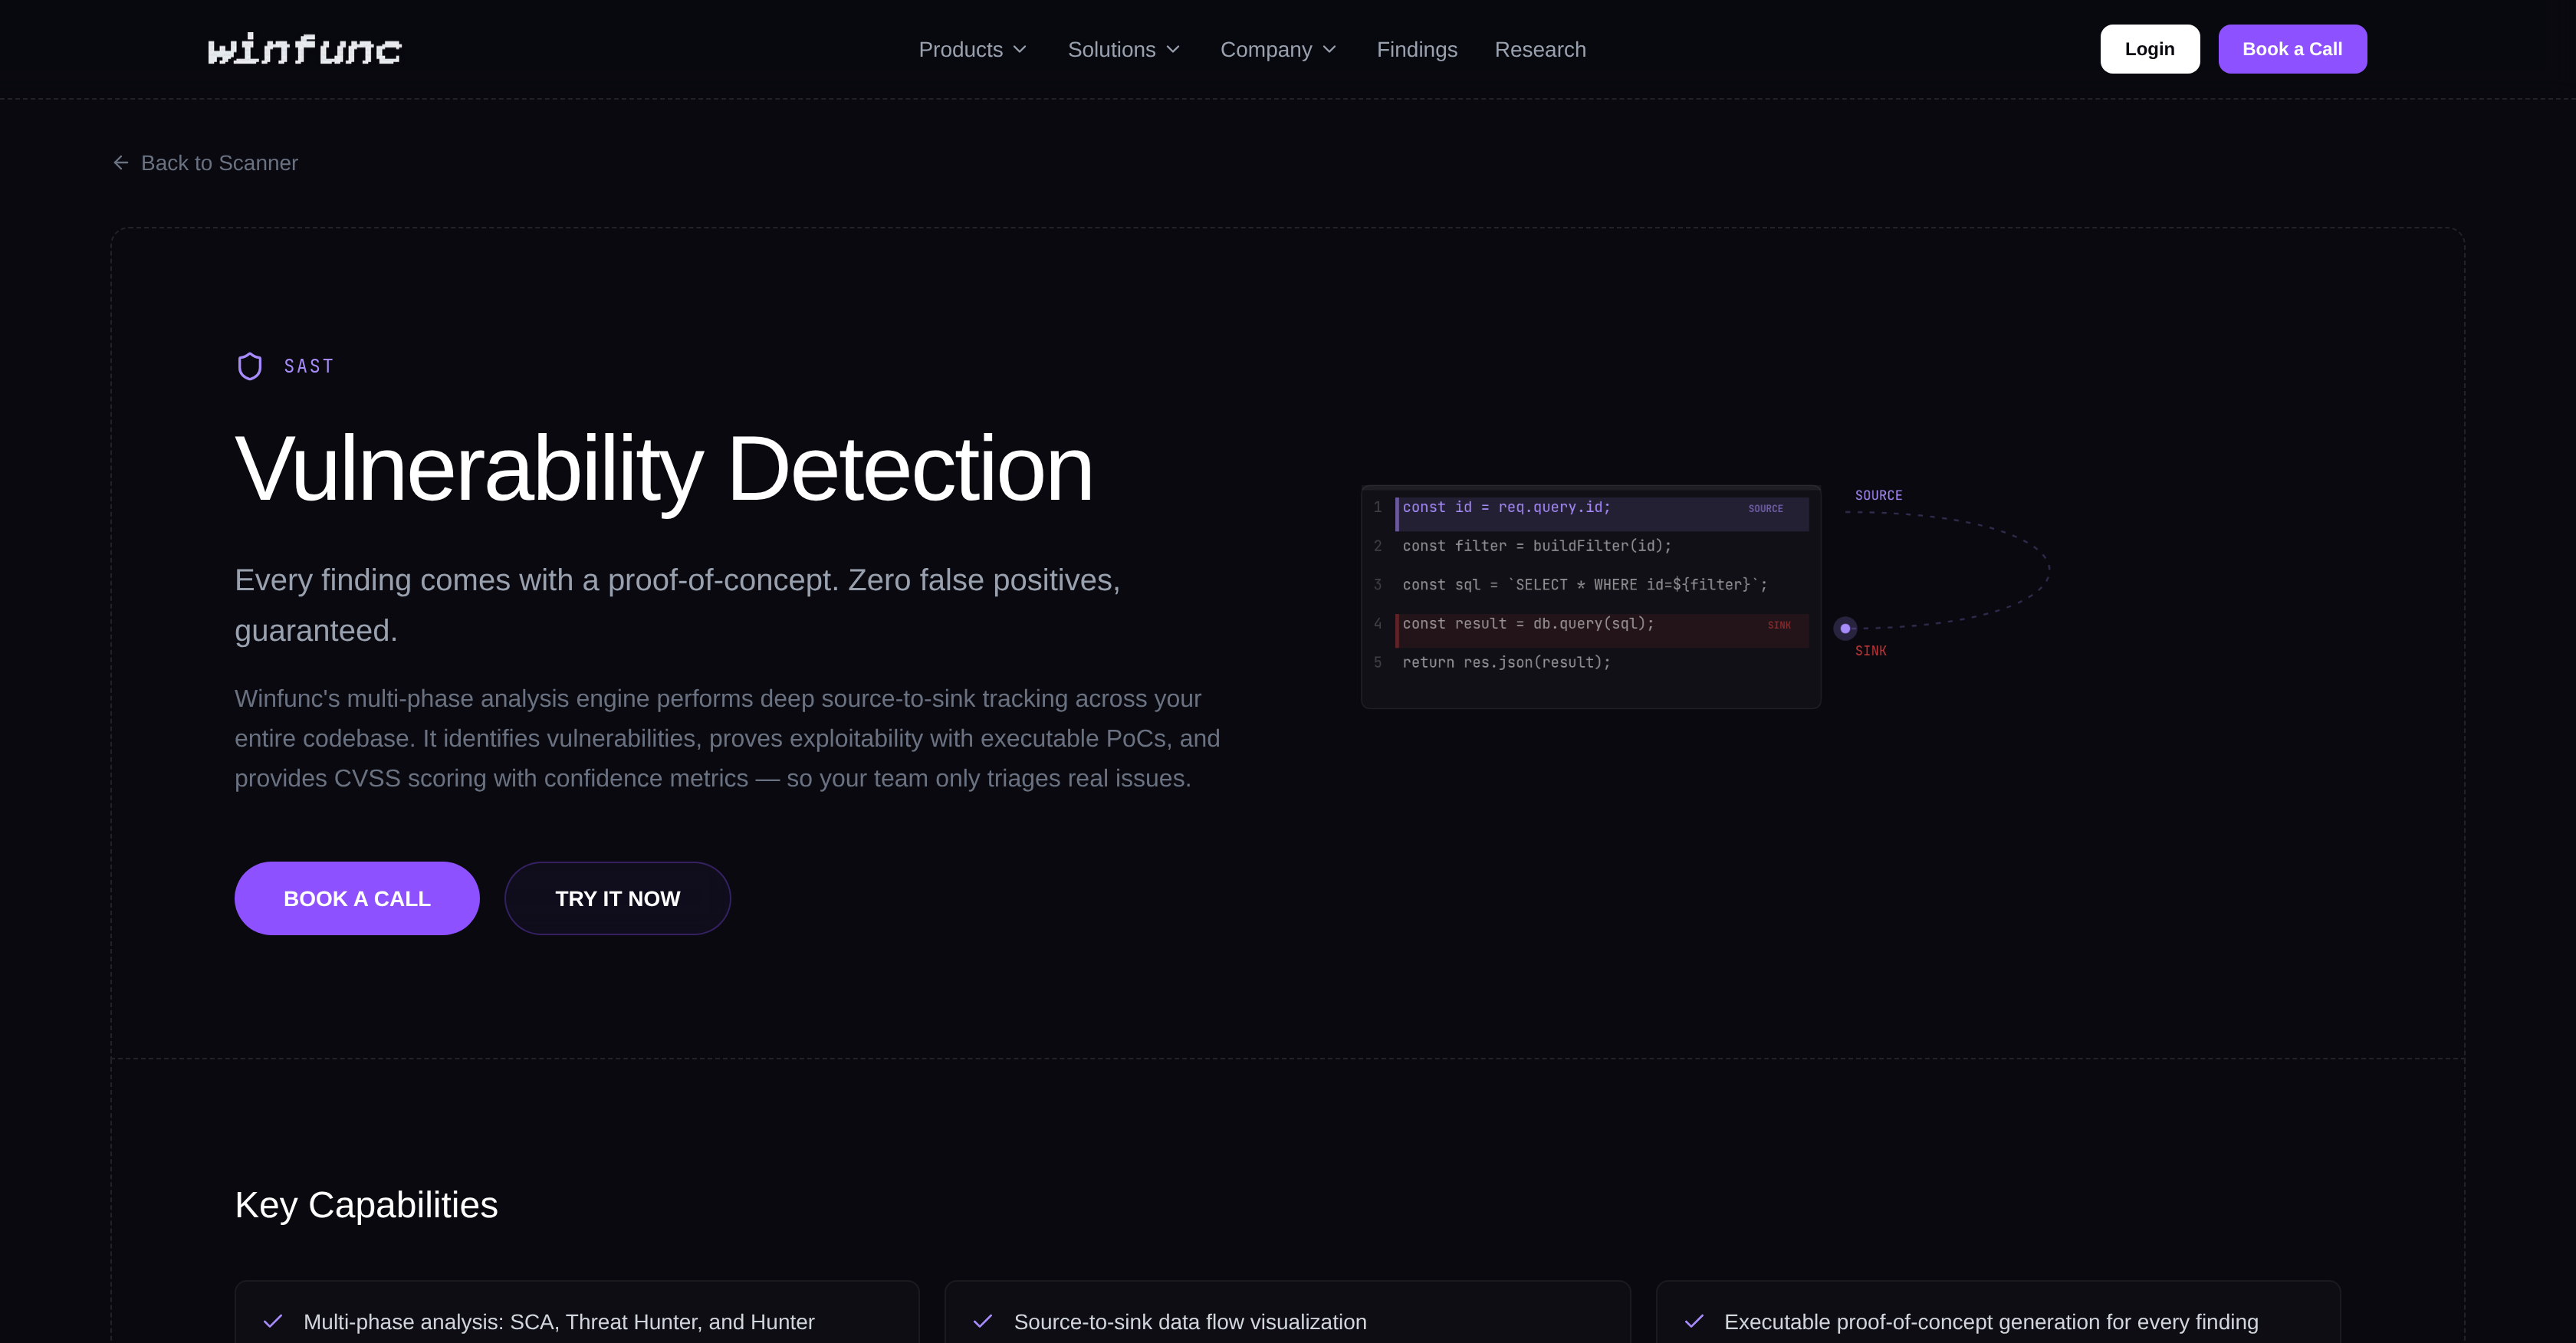
- Eliminate false positives by acting only on verified vulnerabilities with proof-of-concept exploitation and CVSS scoring with confidence metrics.
- Fix business logic flaws like auth bypass and financial manipulation by leveraging full-text search across titles and descriptions to understand your application's specific business flow.
- Visualize the exact attack path from user input to vulnerable code with source-to-sink data flow tracking, so you understand how an attacker exploits your application.
- Prioritize fixes instantly by filtering vulnerabilities by severity, confidence, scan version, and status for a streamlined triage workflow.
- Track every vulnerability from detection to resolution with a full lifecycle system including validation notes, timestamps, and bulk operations for clear team communication.
- Scan only changed files or the entire codebase with incremental and full-codebase scans to match your development pace.
- Eliminate duplicate reports across multiple scans using similarity scoring, saving time and focusing your team on unique fixes.
- Secure codebases in any language—including niche ones like Arc and Haskell—with universal language support that goes beyond pattern matching.
Pros & Cons
Pros
- Finds security vulnerabilities fast
- Comprehensive triage and patching
- Sophisticated multi-phase analysis engine
- In-depth source-to-sink tracking
- Effective identification of vulnerabilities
- Proof-of-concept exploitation provision
- Accurate CVSS scoring
- Eliminates false positives
- Source-to-Sink data flow visualization
- Multi-phase analysis feature
- Smart vulnerability type classification
- Full-text search across descriptions
- Detects business logic vulnerabilities
- Universal language support
- Duplication detection with similarity scoring
- Facilitates incremental and full-codebase scans
- Detailed vulnerability lifecycle tracking
- Understands business flow of application
- Identifies logical flaws in codebase
- Advanced filtering features
- Generates comprehensive reports
- Detects auth bypass vulnerabilities
- Detects financial manipulation vulnerabilities
- Proof-of-concept for each finding
- Visualizes application's data flow
- Race condition and TOCTOU detection
- Status workflow for vulnerabilities
- Formal verification of exploitability
- Tracks changes with diff-based analysis
- Export and print capabilities
- Supports niche languages like Arc and Haskell
Cons
- No mobile application
- Potentially overwhelming interface
- Requires technical expertise
- No offline functionality
- Unclear guidance for beginners
- No described plug-in support
- Complex report interpretation
- No free trial mentioned
- Limited customer support details
Reviews
Rate this tool
Loading reviews...
❓ Frequently Asked Questions
Winfunc is an AI-powered tool designed to find, triage and patch security vulnerabilities in codebases within a short time frame.
Winfunc finds and patches security vulnerabilities by leveraging its sophisticated multi-phase analysis engine. This engine performs deep source-to-sink tracking across an entire codebase to identify vulnerabilities, provide proof-of-concept exploitation, and generate CVSS scoring with confidence metrics.
The role of the multi-phase analysis engine in Winfunc is to perform deep source-to-sink tracking across an entire codebase. This allows it to effectively identify vulnerabilities, provide proofs of concept for exploitation and provide CVSS scoring with confidence metrics.
Winfunc performs source-to-sink tracking by using a sophisticated multi-phase analysis engine which performs a deep tracking across an entire codebase. This engine is capable of tracing the complete data flow from user input to vulnerable code path in the codebase.
Winfunc helps in eliminating false positives by providing proof-of-concept exploitation and CVSS scoring with confidence metrics for each vulnerability it detects. Thus, only real issues are addressed by your team eliminating chances of dealing with false positives.
Winfunc can detect various vulnerabilities like authorization bypass and financial manipulations. It allows in-depth understanding of the application's business flow which enables it to detect logical flaws specific to the codebase.
AI confidence scoring in Winfunc strengthens the reliability of detected vulnerabilities. For each vulnerability, Winfunc provides a confidence score from 0 to 1.0, thereby quantifying the reliability of each detection.
Winfunc facilitates business logic vulnerability detection such as auth bypass and financial manipulation by providing full-text search across titles and descriptions and understanding of the application's business flow beyond pattern matching.
Winfunc can support all major programming languages, including niche ones like Arc and Haskell for finding and patching security vulnerabilities.
The unique offerings of Winfunc include source-to-sink data flow visualization, multi-phase analysis, duplication detection with similarity scoring across scans, incremental and full-codebase scans, and vulnerability lifecycle with sophisticated status tracking.
Winfunc understands the business flow of an application by going beyond pattern matching. This comprehensive approach enables Winfunc to identify logical flaws specific to the codebase, create a clear visualization of source-to-sink data flow, and proactively detect potential threat areas.
Winfunc can identify logical flaws specific to your codebase by understanding your application's business flow beyond simple pattern matching. It dives into details like roles, permissions, financial transactions to identify potential security vulnerabilities.
Yes, with Winfunc's sophisticated source-to-sink tracking system, you can visualize the complete data flow from user input to the vulnerable code path. This helps in fully understanding how an attacker can exploit your application.
Yes, Winfunc does offer advanced filtering features. It provides filtering by severity, confidence, scan version, and status. This makes it easier to triage and take action on the identified vulnerabilities.
Yes, Winfunc can generate comprehensive reports. It makes available professional PDF reports containing triage workflow with status tracking, validation notes, timestamps, and bulk operations. This facilitates clear communication and strategic planning.
Winfunc aids in auth bypass and financial manipulation detection by understanding your application's business flow—roles, permissions, and financial transactions. This way, it identifies logical flaws specific to your codebase which form the backbone for such attacks.
Winfunc's duplication detection feature works by leveraging similarity scoring across scans. The tool can take multiple scans, compare them, and identify the elements that might have been duplicated, thus saving time and encouraging more efficient bug fixing process.
Yes, Winfunc is capable of performing both incremental and full codebase scans. This feature allows for targeted scans on altered files besides the ability to conduct comprehensive audits of the entire codebase.
Winfunc's vulnerability lifecycle tracking is a complete triage workflow with status tracking, validation notes, timestamps, and bulk operations. This feature aids in effective vulnerability management by keeping track of the vulnerability status from detection to resolution.
Yes, given its universal language support capability, Winfunc can certainly help with detection of security vulnerabilities in Arc and Haskell codebases. Irrespective of the programming language used in the codebase, Winfunc's sophisticated analysis can detect and fix potential threats with high accuracy.
Pricing
Pricing model
No Pricing